Iran’s Banks Face a Web Trust Problem as Foreign Certificates Are Revoked
Iran’s central bank is developing a domestic TLS certificate chain after foreign issuers reportedly revoked certificates used by banking services amid sanctions.

Latest from Interview


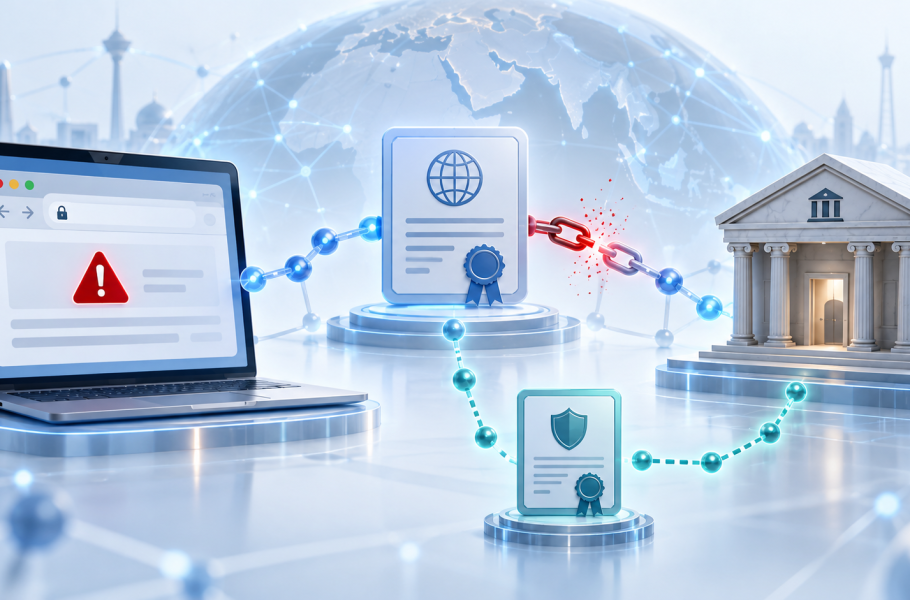
Iran’s central bank says foreign issuers have revoked certificates used by banking services amid sanctions. Its proposed fallback would shift trust to a domestic root that major browsers and operating systems do not recognize by default.
Several Iranian banking websites and digital services have lost security certificates issued by foreign providers in recent weeks, causing browser warnings and, in some cases, disrupting access to web-based banking, according to officials at the Central Bank of Iran.
The central bank is now working on a mechanism that would allow banks to use certificates chained to the existing “Iran Root CA,” reducing their dependence on foreign certificate authorities. Rajabzadeh, the central bank’s head of security and artificial intelligence, said some foreign-issued certificates had been revoked unilaterally, sometimes without advance notice, on the basis of US and European sanctions. Digiato could not independently verify the reason for the revocations, and the affected banks and certificate providers were not identified.
The proposal would not replace the encryption standards used by banks. It would instead change the organization that vouches for the identity of their websites and services. That distinction matters because the Iranian root certificate is not currently trusted by default in widely used browsers and operating systems.
The technology stays the same, but the trust anchor changes
Banks use TLS certificates to prove that a website belongs to the organization named in the certificate and to establish an encrypted connection. When a user opens a banking website, the browser checks the domain name, the certificate’s validity period and whether its chain leads to a root certificate that the browser or operating system already trusts.
Under the central bank’s plan, banking services would continue to use established technologies and standards, including X.509 certificates, secure versions of TLS, recognized cryptographic algorithms and mechanisms for checking and revoking certificates, Rajabzadeh said. The main change would be the certificate issuer and the root of the trust chain.
The central bank is not building a new public-key infrastructure from scratch, according to Rajabzadeh. The Iran Root CA already exists; the regulator’s role is to design and coordinate a mechanism for the banking network to use its certificate chain.
Rouhollah Mohammadkhani, Dotin’s director of security and business continuity, said a “domestic security certificate” is not a separate technical category. A certificate issued under an Iranian authority can use the same encryption standards as one issued by an international provider.
“The main issue is the chain of trust: which body issued the bank’s certificate and who recognizes that body as trustworthy,” Mohammadkhani said.
Why browsers may still show a warning
A technically valid certificate will still trigger a warning if the browser cannot trace it to a root in its trusted store. Individual bank certificates do not need to be added to browsers one by one; the relevant trust anchor is the issuing authority’s root certificate.
Adding a new authority to a public root store is neither immediate nor automatic. Mozilla’s root-store policy requires applicants to meet technical and operational rules, publish certificate-policy documentation and provide continuing audit evidence. Chrome’s inclusion process likewise evaluates an operator’s security practices, audits and value to the wider web before deciding whether to distribute a root certificate.
Mohammadkhani said an authority’s Iranian origin does not by itself prevent it from being used for TLS. Becoming a globally trusted public certificate authority, however, also involves legal, commercial, auditing and security reviews. The central bank has not said whether the Iran Root CA has applied for inclusion in major public trust stores.
Manual installation shifts responsibility to users
Until the Iranian root is included in public trust stores, one option raised by the central bank is for customers to install and trust the root certificate on their own devices. Rajabzadeh said this should happen only after a broad public-awareness campaign and that the certificate should be obtained through an official, verifiable channel.
Installing a root certificate tells a device to trust certificates issued under that chain. That does not automatically mean the encryption is weaker, but it makes the authenticity and governance of the root critical. A fraudulent or compromised root distributed through a fake website, text message or social-media link could cause a device to accept certificates it should reject.
Mohammadkhani urged customers to use only domains announced through their bank’s official channels and, if installation becomes necessary, to obtain the root certificate solely from an official source. Users should not install root certificates received through unfamiliar links, unverified messages or unofficial websites.
The central bank has not provided a deployment timetable, a distribution mechanism or a list of banking services that would move to the domestic chain. It also has not identified the foreign authorities that revoked certificates or published the audits and certificate policies that would allow outsiders to assess the proposed root’s operation. Those details will determine whether the plan becomes a durable alternative or simply moves Iran’s banking trust problem from foreign issuers to users’ devices.